Two nodes. One architecture.
Atlas for services and data. Argos for networking and the perimeter. Two products, two roles with distinct responsibilities.
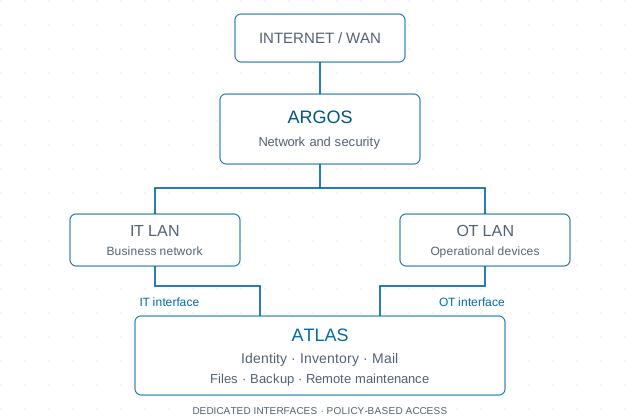
Services and networking have different responsibilities
Atlas orchestrates identity, communication and data; Argos manages the perimeter, networks and site connectivity. They can be evaluated separately: local consoles retain distinct authentication and roles. Argos offers partner access through explicit Citadel pairing. Automatic high availability between appliances is not documented.
Integration through networking
Networks protected by Argos can reach Atlas services through explicit policies and VPN site links. Argos console identity remains appliance PAM; it is not presented as federated Atlas login.
These capabilities are documented in the source; they are not hardware certifications, benchmarks or availability guarantees. Verify configuration and workload during assessment.
Control starts with a conversation.
Tell us about your infrastructure. Let’s start with what you actually need.
Talk to an engineer